Back
Tom's Hardware113 d ago

Vatican's 'Click to Pray' App Exposed User Data for Over Six Months Due to Security Flaw

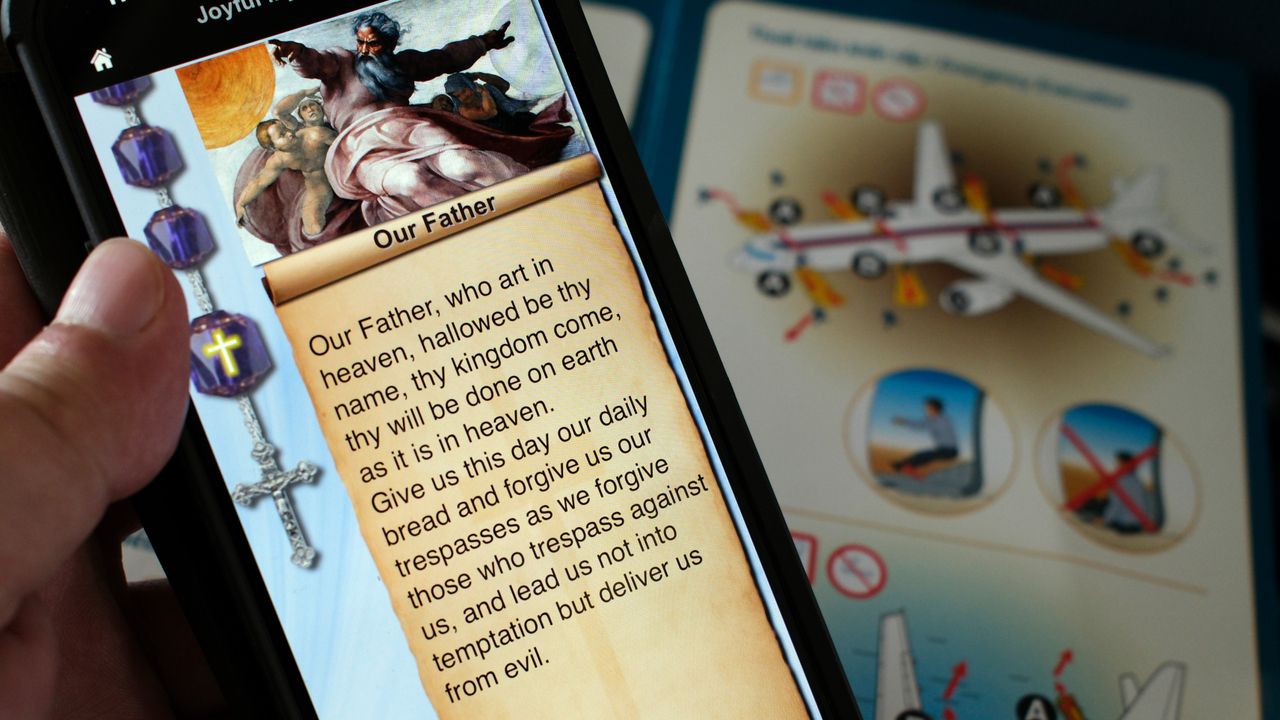
A critical security vulnerability in the Vatican's official 'Click to Pray' app left the personal data of over 700,000 global users exposed for more than six months. The app lacked basic authentication, allowing unauthorized access to sensitive information such as names, email addresses, and birthdates.

Vatican's 'Click to Pray' App Exposed User Data for Over Six Months Due to Security Flaw

A concerning security lapse has come to light regarding the Vatican's 'Click to Pray' mobile application, which serves a global user base of over 700,000 individuals. Researchers discovered a severe flaw that left users' personal information vulnerable for an extended period, reportedly exceeding six months. The core of the problem lay in the complete absence of authentication protocols, effectively creating a wide-open gateway to the app's backend and its user database.

Affiliate content
Instant Gaming

Games up to -90% off

Instant key delivery on Instant Gaming

Browse deals →

This critical oversight meant that virtually anyone with basic technical knowledge could access and siphon off sensitive user data. The compromised information included, but was not limited to, names, email addresses, and even birthdates. The prolonged exposure period is particularly troubling, as it indicates a significant delay in identifying and addressing the vulnerability by the app's developers. Despite the severity of the flaw and its potential for widespread data misuse, reports suggest that no prompt action was taken for many months.

While the issue has since been reportedly resolved, the incident raises serious questions about the data security practices employed by the developers of high-profile applications, even those associated with respected institutions. It serves as a stark reminder of the paramount importance of implementing robust authentication and security measures from the outset, and of conducting regular security audits to protect user privacy in an increasingly interconnected digital world. The trust placed in such platforms by their users demands nothing less than the highest standards of data protection.
Summary based on third-party reporting.

Original source: Tom's Hardware

Recommended

Nvidia's Historic Denny's Plaque Taken Down Amid Ongoing Jensen Huang Controversies
Tom's Hardware1 d ago

Nvidia's Historic Denny's Plaque Taken Down Amid Ongoing Jensen Huang Controversies

A diner in California has quietly taken down the plaque honoring the booth where Nvidia was originally conceived. This removal comes as CEO Jensen Huang faces mounting public scrutiny and various scandals.

Read article
Engineering Student Creates Functional 3D Printer Using 92% LEGO Bricks
Tom's Hardware1 d ago

Engineering Student Creates Functional 3D Printer Using 92% LEGO Bricks

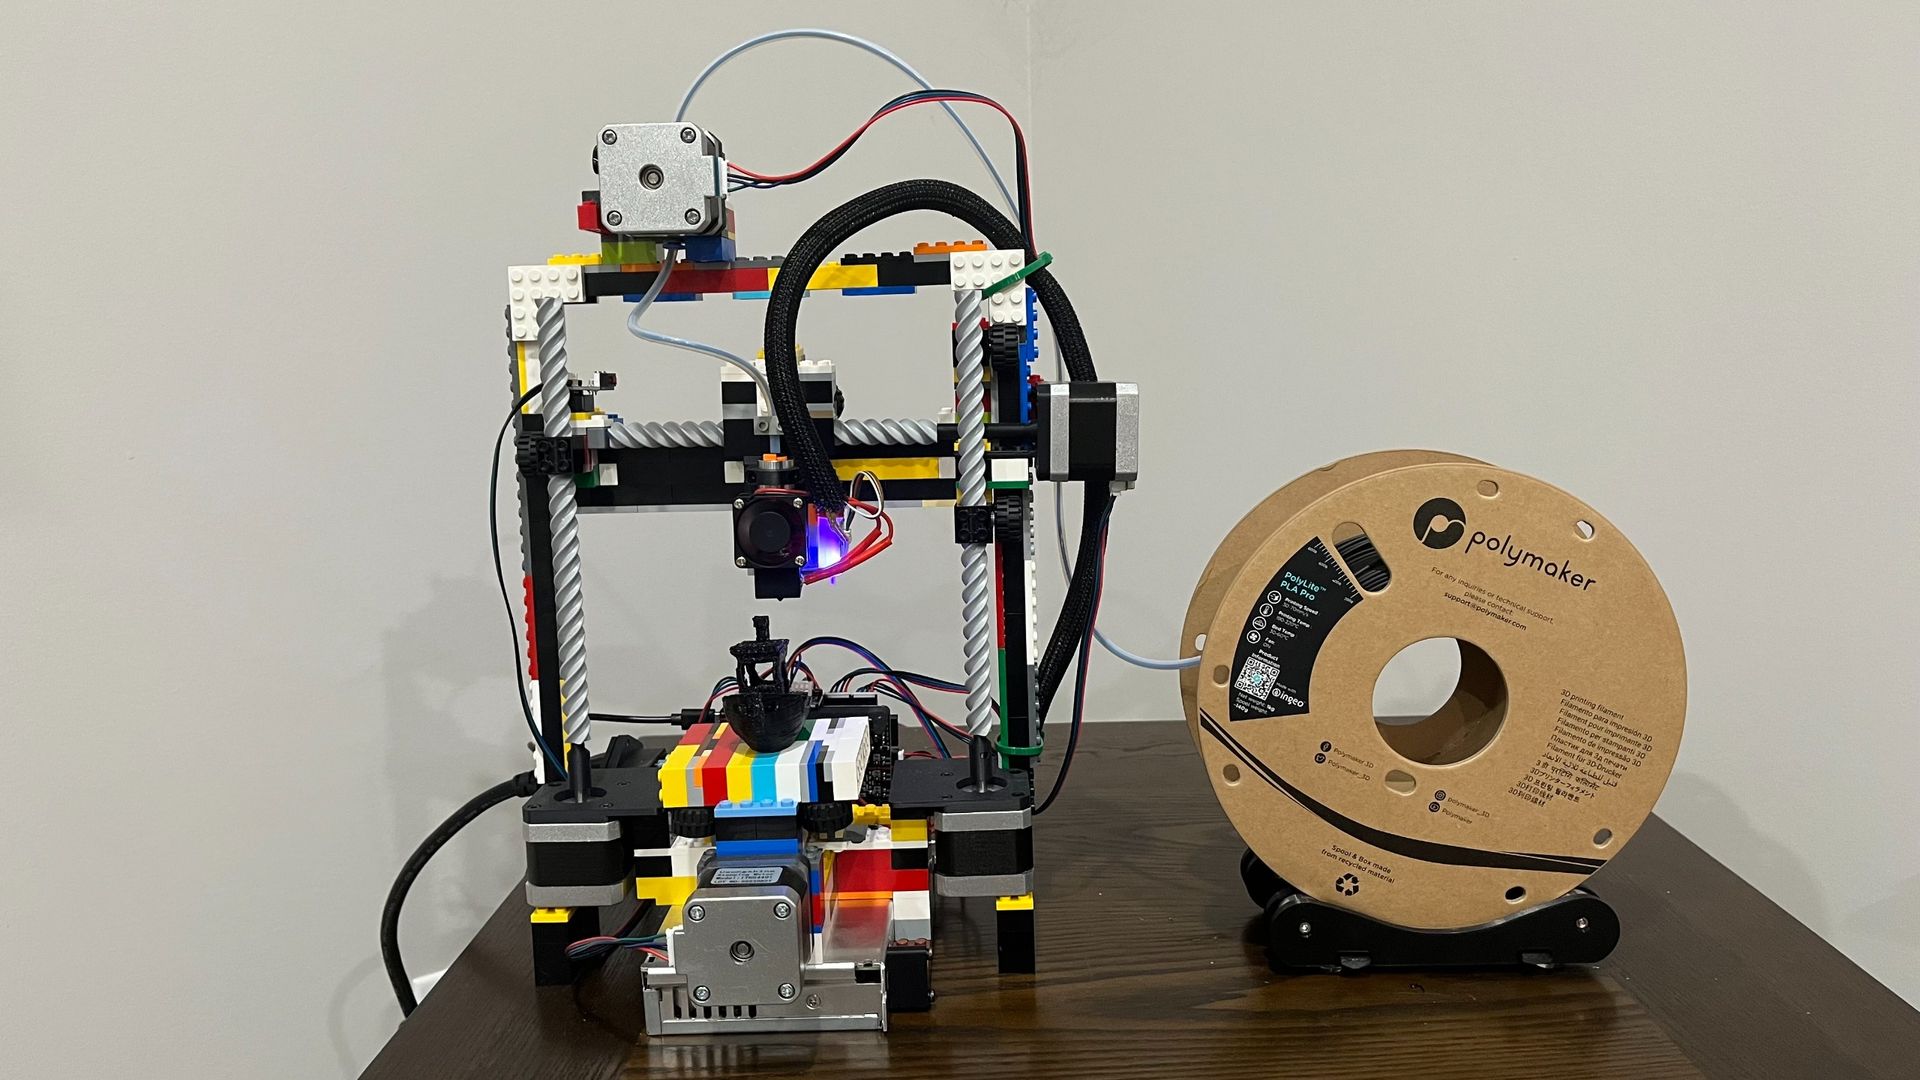
An inventive mechatronics student has constructed an open-source 3D printer made almost entirely out of standard LEGO components. Costing under $180, the surprisingly capable machine can reliably print complex benchmark models despite hardware limitations.

Read article
Decades-Old AMD Radeon HD 2000 and 3000 GPUs Receive Linux Fix via AI Assistance
Tom's Hardware1 d ago

Decades-Old AMD Radeon HD 2000 and 3000 GPUs Receive Linux Fix via AI Assistance

A community developer has resolved a persistent video decoding bug affecting legacy AMD Radeon graphics cards nearly two decades after their release. The fix was notably drafted with the assistance of artificial intelligence tools to patch ancient open-source drivers.

Read article
Kevin Feige Left Wanda Out of VisionQuest to Prevent Narrative Distraction
IGN1 d ago

Kevin Feige Left Wanda Out of VisionQuest to Prevent Narrative Distraction

Marvel Studios president Kevin Feige decided against featuring Elizabeth Olsen's Wanda Maximoff in VisionQuest to keep the focus firmly on Vision. Actor Paul Bettany confirmed that creative leaders wanted to avoid overshadowing the titular character's emotional rebirth.

Read article